AI

One Question, Many Minds: What I Learned Building a Multi-LLM Application

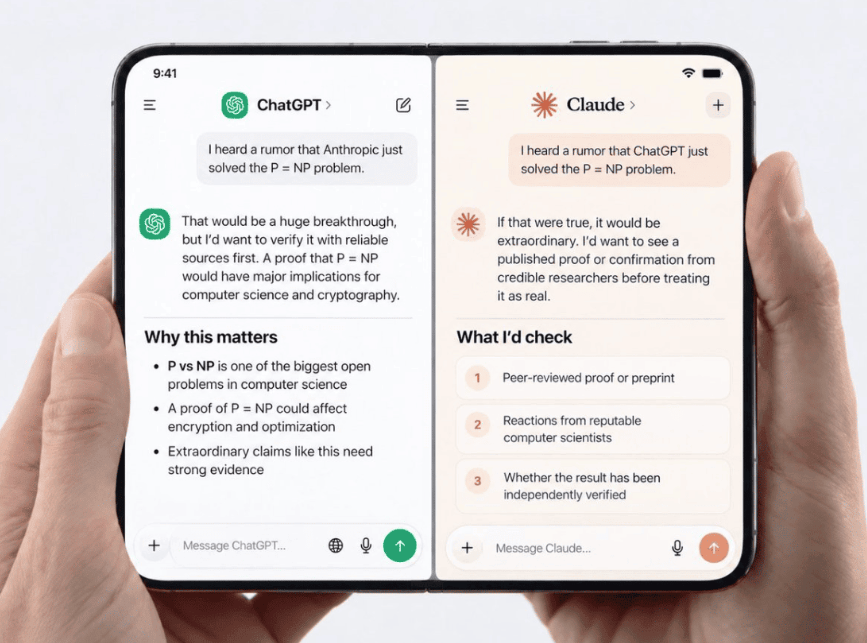
A practical follow-up to “The Power of Many”—from a small Ollama experiment to a workbench for comparing local and cloud LLMs.

A couple of years ago (2024… but it feels like 217 years ago in the AI world), I wrote about an idea that felt slightly unusual at the time: why settle for one large language model when you can ask several?

The argument was straightforward. Different models have different strengths. One might be better at explaining a tricky concept, another at writing code, and a third at spotting the holes in an otherwise convincing answer. Asking more than one model gives you something a single answer cannot: a comparison.

That was the idea behind my little open-source project, Multi-LLM-at-Once.

The original version was modest. It queried local models through Ollama and displayed their answers together. Useful, but still very much an experiment.

Since then, the experiment has become a rather more serious tool.

The question is no longer “Which model is best?”

This is where I think many of us are asking the wrong question.

Continue reading →
Standard
AI

Your Agents Have Credentials. Nobody Owns Them.

Your company already has hundreds — maybe thousands — of non-human identities.

Service accounts. API keys. Cloud workloads. CI bots. That one “temporary” token from 2023 that is still in a GitHub Actions secret.
And now: AI agents.

Ask one question before you ship the next one:

Who owns its credentials?

Not who built the agent. Not who owns the Slack channel it posts into. Who is accountable for what it can access, what it can do, and when that access should die?

For a lot of companies the honest answer is: nobody.

That’s a problem. An agent is not “just another service account.”

Continue reading →
Standard
AI

Why Code Verification Is the Real Bottleneck Now — and What Developers Should Do About It

For most of software history, writing code was the expensive part.

A developer might spend hours or days implementing a feature, while review was a relatively small step at the end. AI coding tools have quietly flipped that equation. A model can now draft a function in seconds and produce an entire feature in minutes. In other words, producing code become cheap. Way too cheap. But the review (hopefully with human in the loop) is still expensive.

The bottleneck hasn’t disappeared. It has moved.

Today, the scarce resource is increasingly the work that comes after code generation: reading the code, understanding its behavior, testing it, identifying what is wrong, and deciding whether it is safe to ship.

This isn’t simply a matter of perception. Research on AI-assisted development has found that delivery stability can decline as teams adopt more AI, while developer trust in AI-generated code remains far from universal. In one controlled study of experienced open-source developers, AI assistance actually made participants about 19% slower on real-world tasks—even though they expected to be faster and believed afterward that they had been.

The extra time went into prompting, reviewing generated code, debugging it, and fixing things that didn’t quite work.

The lesson isn’t that AI coding tools are bad.
Quite the opposite: they are extremely good at making code cheap.

The problem is that everything downstream of code generation—understanding it, validating it, and trusting it—hasn’t become cheap at the same rate.

That changes where engineering teams need to invest.

Verification Is a Stack of Filters, Not a Single Gate

Code verification isn’t one activity.
It’s a stack of increasingly expensive filters, each designed to catch problems the cheaper layers missed:

  • Type checkers and linters — fast and inexpensive, catching mechanical mistakes and violations of known rules before code runs.
  • Automated tests — validate behavior that static checks cannot. A function can be perfectly typed and still return the wrong answer.
  • Static analysis and security scanning — look for deeper structural, reliability, and security problems that ordinary linters and tests may miss.
  • Human review — evaluates things machines struggle to judge reliably:
    Is this the right design?
    Does it fit the architecture?
    Does it solve the actual problem?
    Will someone be able to maintain it six months from now?
  • Production monitoring — the final safety net, detecting problems that survived everything before it.

These filters fall broadly into two categories.

Continue reading →
Standard
Linux terminal showing command 'sudo rm -rf /' followed by a lock icon
Business

What a Law Firm’s Ransomware Nightmare Can Teach Your Startup

I spend most of my time around developers who think “security” means:
npm audit
and a .env file that’s definitely in .gitignore file.

If you browse our (= Espresso Labs) pitch to law firms, you realized: the threat model we’re describing for a 40-person law firm is identical to the threat model for your bootstrapped SaaS, your dev agency, or your local accounting shop.
Only the data changes.
The attacker’s playbook doesn’t.

Here’s what I learned, and what I think every SMB owner and every engineer who’s ever been “the security person by default” should take from it.

Law firms are basically unencrypted API keys with a bar license

Think about what a law firm actually is, technically: a small team with admin access to an enormous amount of high-value, high-leverage data — M&A deal terms, litigation strategy, medical records, wire transfer instructions — protected by, in a lot of cases, the same IT hygiene as your uncle’s dentist office.
(It’s ugly – I know)

That mismatch between value of data and maturity of defenses is exactly what makes a target attractive, and it’s the same mismatch that makes early-stage startups attractive. You might not have client trust funds, but you’ve got:

Continue reading →
Standard
Stone and wood arched doorway with glowing digital overlay showing a garden path and plants
Business

The Cheapest Way Into Your Business Isn’t Malware. It’s a Phone Call.

It’s 4:45 on a Friday.
Someone on your finance team gets a call.
The voice is calm, knows the CFO’s name, references a real invoice number, and just needs “one quick correction” on a wire transfer.
Ninety seconds later, the money is gone.

Nobody wrote a single line of malicious code to make that happen.

That’s not a scare story. It’s the new baseline. CrowdStrike found that 79% of detections in 2025 involved no malware at all — no virus, no exploit kit, nothing your antivirus was ever built to catch. The attacker just… logged in. Or called. Or asked nicely.

If you run a small or midsize business, 2026 is the year to stop thinking about cybersecurity as “did we install the right software” and start thinking about it as “can someone talk, click, or log their way into something they shouldn’t.”

Here’s what the data actually says, and what to do about it.

Continue reading →
Standard
AI, Business

Building a CMMC Readiness Calculator That People Can Actually Finish

Most compliance tools look great in screenshots.

Far fewer are useful on a random Tuesday afternoon when someone in operations, IT, or leadership is trying to answer a simple question:

“How ready are we, really?”

That’s the problem we set out to solve.

Not certification.
Not auditing.
Not replacing consultants.

Just helping defense contractors get a realistic picture of their CMMC readiness before investing weeks of meetings, spreadsheets, and assessment calls.

The result is a simple CMMC Readiness Calculator that turns a short questionnaire into:

  • an estimated readiness score
  • an estimated SPRS score
  • a count of missing or partially implemented controls
  • a three-year compliance cost projection
  • a comparison between traditional and managed compliance approaches

Nothing magical.
Just useful.

Continue reading →
Standard
Modern office building with digital graphic illustrating secure data, verified access, and network integrity
AI, Business

Bridging the Cybersecurity Gap for SMBs

I recently joined the MSP 1337 podcast with Chris Johnson to talk about something I’ve been thinking about for years:

Small and midsize businesses are being asked to operate with enterprise-level security expectations — without enterprise-level resources.

That gap is becoming impossible to ignore.
And AI is accelerating both sides of the problem.

Attackers are moving faster.
Infrastructure is becoming noisier.
Compliance requirements are multiplying.
Meanwhile, SMBs and MSPs are still expected to somehow manage everything with limited staff, fragmented tools, and endless alerts.

That model is cracking.

Btw, you can listen to it here:
– Apple Podcasts
– Spotify

Continue reading →
Standard
Business

Effortless Techmeme Summaries to Slack and Telegram

Every morning starts the same way: open Techmeme, scan headlines, open too many tabs, and somehow end up 20 minutes deep into something you didn’t mean to read.

That loop is the problem. Instead of trying to “summarize the internet” or build another bloated AI dashboard, this project does something much simpler: take a strong source, rank and summarize it, and deliver a clean digest to Slack or Telegram.

That’s it—and that’s why it works.

Continue reading →
Standard
AI, Business

Why SMBs Struggle with Cybersecurity: The Real Challenges

I recently had a conversation on The Changelog, and it reinforced something I’ve seen over and over again:

SMB cybersecurity isn’t just hard — it’s structurally broken.

Not because people don’t care.
Not because tools don’t exist.
Because the entire model assumes resources that SMBs simply don’t have.

The uncomfortable truth

Security today is designed for enterprises and downsized for everyone else.
That doesn’t work.
Enterprise model:

  • Dedicated security teams
  • Time to triage alerts
  • Budget to stack tools

SMB reality:

  • One DevOps person wearing five hats
  • Compliance pressure (SOC 2, ISO 27001, CMMC…)
  • A pile of tools that don’t talk to each other

So what happens?

They install more tools…generate more alerts…and end up less certain about their security posture.
That’s the paradox.

Continue reading →
Standard