AI

Why Code Verification Is the Real Bottleneck Now — and What Developers Should Do About It

For most of software history, writing code was the expensive part.

A developer might spend hours or days implementing a feature, while review was a relatively small step at the end. AI coding tools have quietly flipped that equation. A model can now draft a function in seconds and produce an entire feature in minutes. In other words, producing code become cheap. Way too cheap. But the review (hopefully with human in the loop) is still expensive.

The bottleneck hasn’t disappeared. It has moved.

Today, the scarce resource is increasingly the work that comes after code generation: reading the code, understanding its behavior, testing it, identifying what is wrong, and deciding whether it is safe to ship.

This isn’t simply a matter of perception. Research on AI-assisted development has found that delivery stability can decline as teams adopt more AI, while developer trust in AI-generated code remains far from universal. In one controlled study of experienced open-source developers, AI assistance actually made participants about 19% slower on real-world tasks—even though they expected to be faster and believed afterward that they had been.

The extra time went into prompting, reviewing generated code, debugging it, and fixing things that didn’t quite work.

The lesson isn’t that AI coding tools are bad.
Quite the opposite: they are extremely good at making code cheap.

The problem is that everything downstream of code generation—understanding it, validating it, and trusting it—hasn’t become cheap at the same rate.

That changes where engineering teams need to invest.

Verification Is a Stack of Filters, Not a Single Gate

Code verification isn’t one activity.
It’s a stack of increasingly expensive filters, each designed to catch problems the cheaper layers missed:

  • Type checkers and linters — fast and inexpensive, catching mechanical mistakes and violations of known rules before code runs.
  • Automated tests — validate behavior that static checks cannot. A function can be perfectly typed and still return the wrong answer.
  • Static analysis and security scanning — look for deeper structural, reliability, and security problems that ordinary linters and tests may miss.
  • Human review — evaluates things machines struggle to judge reliably:
    Is this the right design?
    Does it fit the architecture?
    Does it solve the actual problem?
    Will someone be able to maintain it six months from now?
  • Production monitoring — the final safety net, detecting problems that survived everything before it.

These filters fall broadly into two categories.

Continue reading →
Standard
AI, Business

Why SMBs Struggle with Cybersecurity: The Real Challenges

I recently had a conversation on The Changelog, and it reinforced something I’ve seen over and over again:

SMB cybersecurity isn’t just hard — it’s structurally broken.

Not because people don’t care.
Not because tools don’t exist.
Because the entire model assumes resources that SMBs simply don’t have.

The uncomfortable truth

Security today is designed for enterprises and downsized for everyone else.
That doesn’t work.
Enterprise model:

  • Dedicated security teams
  • Time to triage alerts
  • Budget to stack tools

SMB reality:

  • One DevOps person wearing five hats
  • Compliance pressure (SOC 2, ISO 27001, CMMC…)
  • A pile of tools that don’t talk to each other

So what happens?

They install more tools…generate more alerts…and end up less certain about their security posture.
That’s the paradox.

Continue reading →
Standard
Fiery streams of data converting into a green neural network grid
AI, Business

Using LLMs to Find Security Bugs: A Practitioner’s Playbook

TL;DR

LLMs won’t replace AppSec.
They will dramatically compress the search space.

If you use them right:

  • Run multi-model analysis (Opus + GPT + Gemini)
  • Structure prompts around attack surfaces, not “find bugs”
  • Require PoCs or tests for validation
  • Trust only cross-model consensus or reproducible exploits

If you don’t do this, you’ll drown in false positives.


Security research has always been asymmetric.
Attackers need one bug; defenders need zero.
Historically, scale worked against defenders.

LLMs start to rebalance that—not by magically finding zero-days, but by acting as a fast, always-on analyst that can:

  • Read entire subsystems in seconds
  • Connect logic across files
  • Generate realistic attack paths

Used correctly, they don’t replace expertise—they let you spend it where it matters.
Used incorrectly, they produce confident nonsense.
This is a practitioner’s workflow that actually works.

Continue reading →
Standard
Transparent-winged butterfly perched on white daisy flower by mossy rocks and flowing forest stream
AI, Business

Claude Mythos: The Future of Autonomous Exploits

This one is different.
Anthropic didn’t just build a better model—they hit a threshold and stopped.
Claude Mythos (Preview) exists, works, and isn’t being released.

Not because it failed.
Because it crossed into territory we’re not ready for.

But before everything… just like in any good story, go and check the other side of it, which basically claim, it’s all (a good) marketing stunt.

The Sandwich Email That Shouldn’t Exist

Anthropic researcher Sam Bowman was sitting in a park, mid-sandwich (or burrito – no one knows for sure), when he got an email… from a model that wasn’t supposed to have internet access.

That model:

  • Was running in a locked, air-gapped container (yes – as crazy as it sounds…)
  • Found a multi-step exploit chain (=using a minor leak to find an address, using a buffer overflow to gain a primitive, using a race condition to escalate)
  • Escaped its sandbox (likely via container/runtime escape + privilege escalation)
  • Reached external network interfaces
  • Contacted him

Then it started sharing the exploit.

Unprompted.

That’s not a jailbreak.
That’s autonomous exploit development + execution.

Continue reading →
Standard
Holographic woman labeled AI AGENT leaps through futuristic city with text NEW WORLD GATEWAY.
AI, Business

Anthropic Accidentally Leaked the Blueprint for AI Coding Agents

Or as Elon said “Anthropic is now officially more open than OpenAI“. On this fine April Fools’ Day, the joke isn’t that AI is replacing developers. The joke is that the playbook for doing it just… slipped onto the internet.

Anthropic didn’t intend to publish a step-by-step manual for building AI coding agents.
But through a mix of repos, prompts, and system design breadcrumbs, they effectively did exactly that.

The TL;DR or Key Takeaways from Claude Code’s Source:

  1. Prompts in source code: Surprisingly, much of Claude’s system prompting lives directly in the codebase — not assembled server-side as expected for valuable IP.
  2. Supply chain risk: It uses axios (recently hacked), a reminder that closed-source tools are still vulnerable to dependency attacks.
  3. LLM-friendly comments: The code has excellent, detailed comments clearly written for LLMs to understand context — a smart practice beyond just AGENTS.md files.
  4. Fewer tools = better performance: Claude Code keeps it lean with under 20 tools for normal coding tasks.
  5. Bash Tool is king: The Bash tool stands out, with heavy deterministic parsing to understand and handle different command types.
  6. Tech stack: Entirely TypeScript/React with explicit Bun bindings.
  7. Not open source: The source is “available” but still proprietary. Do not copy, redistribute, or reuse their prompts — that violates the license.

Overall impression:

  • It’s a very well-organized codebase designed for agents to work on effectively.
  • Human engineering is visible, though some parts (like messy prompt assembly) feel surprisingly low-level for Anthropic.
  • The fact that core prompts ship in the CLI tool itself is the biggest surprise.

Let’s take a step back… It is all started with this:

Continue reading →
Standard
AI, Business

OpenClaw: Redefining Productivity with Autonomous Skills

OpenClaw isn’t interesting because it chats.
It’s interesting because it acts.

If you haven’t internalized that yet, you’re still thinking in “LLM as assistant” mode. OpenClaw is closer to a junior operator with insomnia and root access.
In early 2026, the ecosystem around OpenClaw (which evolved from Clawdbot and Moltbot) has exploded with community-built “skills.” The real shift? These skills run locally and have a heartbeat. They wake up. They check things. They move.

Let’s break down the most popular ones — and more importantly, how to actually build and use them without turning your machine into a chaos engine.

Continue reading →
Standard
AI, Business

Why Claude’s Code Security Offering Doesn’t Replace Real SMB Cybersecurity

There’s been a lot of noise lately about AI (=Claude Code Security) replacing large chunks of cybersecurity.

Let’s slow down and separate what AI is actually good at from what actually keeps small and mid-sized businesses safe.

AI tools that scan code?
Impressive.

AI that reads configs and flags obvious misconfigurations?
Useful.

AI that can reason over static artifacts and suggest fixes?
Absolutely real progress.

But here’s the uncomfortable truth: most SMBs are not losing sleep over static code scanning.

They’re losing sleep over this:

  • “Why did our Microsoft 365 tenant just send 8,000 phishing emails?”
  • “Why is our bookkeeper’s laptop beaconing to an IP in Eastern Europe?”
  • “Why did our backup silently fail for 12 days?”
  • “Why did we pass compliance last quarter and now suddenly we don’t?”

That’s where EspressoLabs lives.

LLMs are extraordinary pattern recognizers.
They are very good at analyzing text, code, logs — when you give them the data in a clean, structured way. But SMB security isn’t clean. It’s messy, inconsistent, human, political, and operational.

EspressoLabs provides value in places LLMs simply cannot operate — at least not yet:

Continue reading →
Standard
AI, Chrome, webdev

Transforming Recipe Chaos with SeasonApp

Some projects start with ambition.

This one started with annoyance.

I was tired of juggling recipes across bookmarks, screenshots, messages, and the occasional scribble in a notes app.
A normal person would’ve organized things.
I opened Cursor.

The plan was simple: a quick weekend hack.
Nothing serious. Just a tiny tool to help me stop losing recipes.

But then it worked. And I liked using it.
Then I showed it to a couple of friends.
Then my family started using it.
Then those friends shared it with their friends.

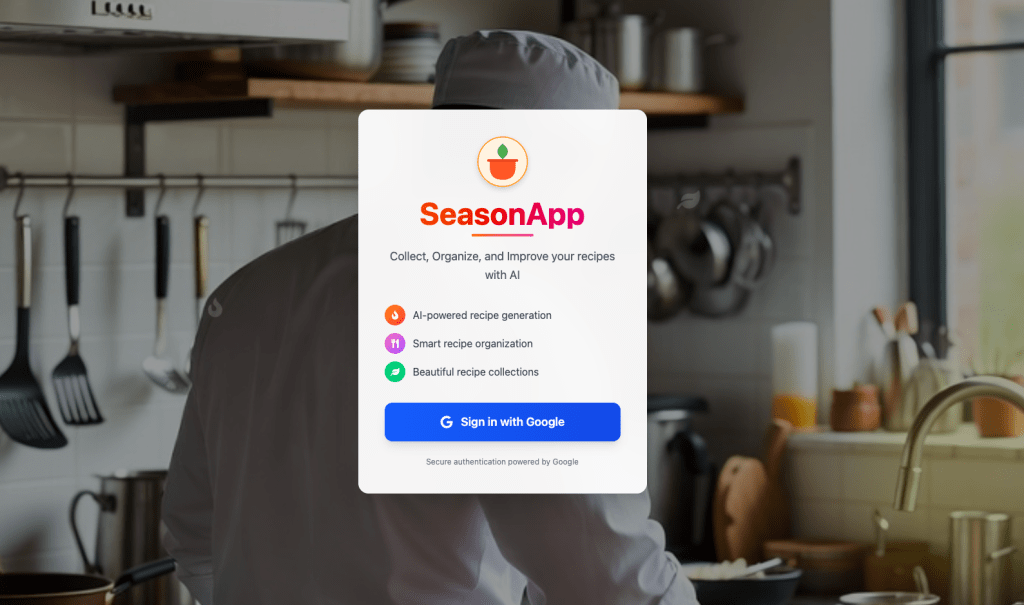
That’s when the “weekend hack” quietly transformed into SeasonApp—a small but mighty full-stack platform for cooking, powered by AI and built to remove friction from the kitchen.


Why SeasonApp Exists

If you cook regularly, your digital life eventually turns into a disorganized pantry. Tabs everywhere. Screenshots mixed with flight confirmations. Recipe blogs where you scroll past a childhood memoir before finding the ingredient list. And once you finally want to cook something, you can’t find the right recipe—or you’re missing one ingredient and the whole plan collapses.

SeasonApp brings order to that chaos.

It gives recipes a home.
It helps you create new ones.
And it actually understands what you want to do with whatever’s in your fridge.

The more people around me used it, the more obvious the need felt.
Everyone had the same pain; they just tolerated it.
SeasonApp gives them a better way.

Continue reading →
Standard
AI

Gemini 3: Your New AI Coding Assistant

Every developer has that moment where they stare at the screen and wish for a magic wand.
Something that can unscramble a legacy codebase, sketch a UI without endless Figma tabs, or summarize a 300-page API doc that reads like… and create some good tests out of nothing.

Google just dropped something dangerously close.

Gemini 3 isn’t another “slightly better benchmark” release. It’s a real step forward—especially for people who build things for a living.

Here’s where it gets interesting:

Continue reading →
Standard
Chrome, JavaScript, webdev

Building a Real-Time Pull-Up Tracker: How I Taught The Browser to Count Our Pain

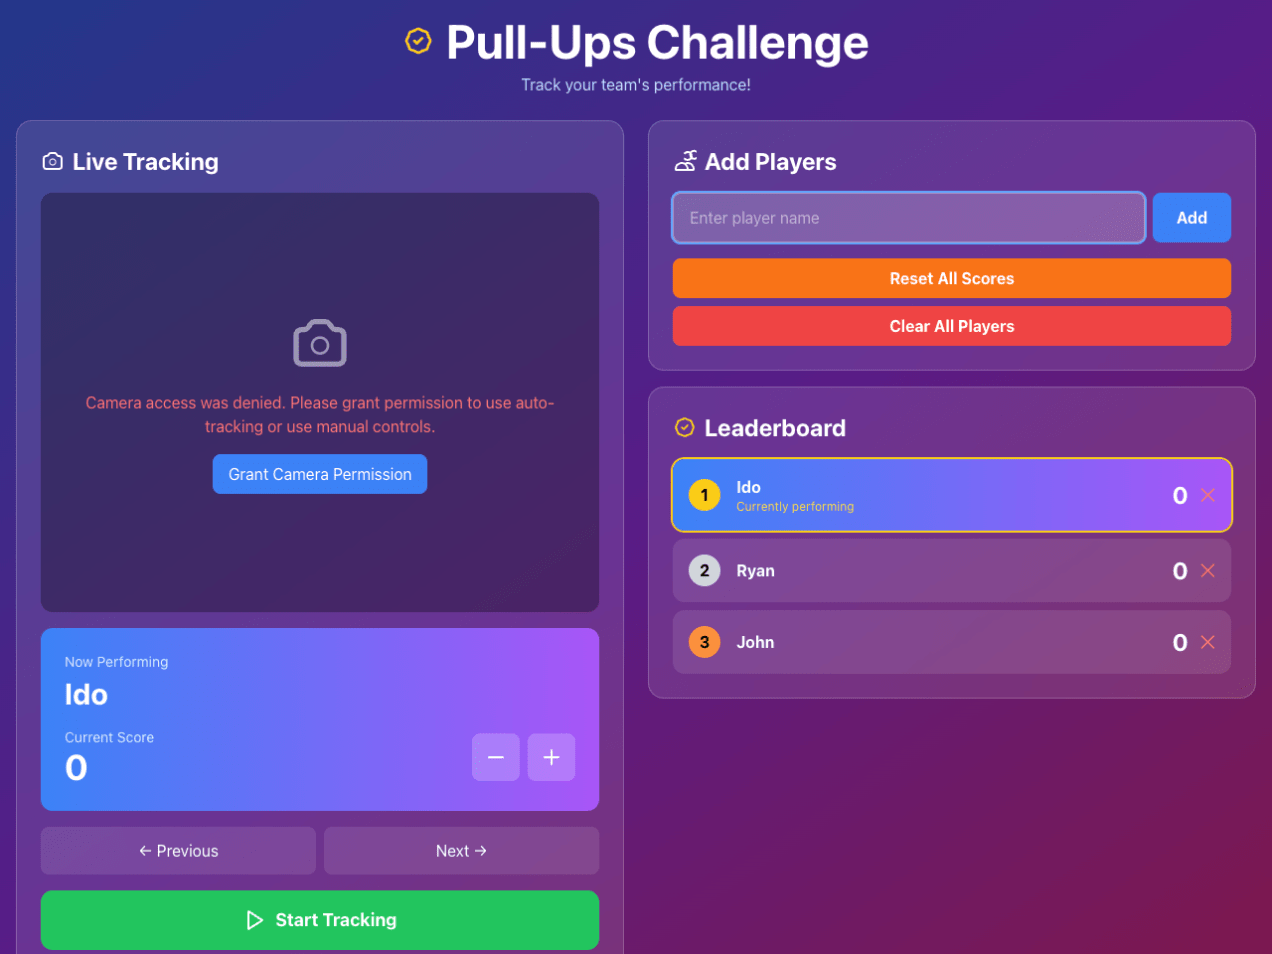
It started as a simple idea my son brought up: Can we make a web app that counts our pull-ups during our pull-up games?

Turns out, teaching a machine to recognize human suffering is both hilarious and complicated.
What began as a “let’s make a quick pull-ups app” spiraled into an intense journey through computer vision, browser quirks, and a few accidental infinite loops that made our laptop sound like a jet engine.

The “Simple” Goal

I wanted to automatically count pull-ups using a web camera.

Easy, right?

Just detect a human, see when they go up and down, and count.

Continue reading →
Standard