Business

The AI Capability Funnel: Why Everyone Is Experiencing a Different Technology

…or if you like the good/old one: The future is here it’s just not evenly distributed — and this time it’s on AI (or SI as from last week).

There is a growing disconnect in the AI/SI conversation, and it’s not because one side is wrong. It’s because people are having radically different experiences with the same technology.

Andrej Karpathy has been pointing at this for months, but his latest framing makes the problem particularly clear: the gap between what people think frontier AI can do and what it can actually do is widening, not closing. He describes a steep capability funnel, with most people near the wide end and a tiny group at the narrow end experiencing something that looks almost like a different technology.

Consider the distribution.
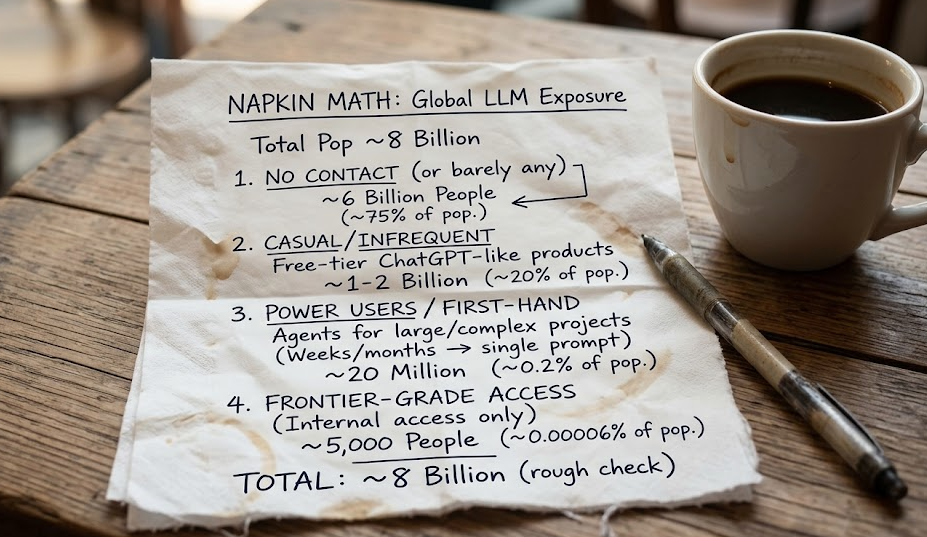
Around six billions people have barely touched AI. Another billion or two use free chat interfaces for search, writing, brainstorming, and the occasional questionable answer. For them, ChatGPT AI is useful, sometimes impressive, but hardly revolutionary.

Then there are roughly 20 million people, many working in technical fields, using paid frontier models and agentic tools on serious, multi-day projects. They are handing agents entire codebases, complex mathematical problems, and substantial research tasks that once required weeks of focused human effort. Increasingly, they return to find much of the work done.

At the very narrow end are perhaps a few thousand people with (free!) access to the latest internal systems. They are experimenting with fleets of agents working for days or weeks on substantial software and research projects, including security-sensitive work such as vulnerability discovery and exploit development.

These numbers should be understood as estimates illustrating the distribution, not a precise census. The important point isn’t whether the boundaries are exactly right. It’s how dramatically the experience changes as you move down the funnel.

And that’s where things get interesting.

Continue reading →
Standard
AI

The Dependency You Didn’t Choose

AI coding agents are making software supply-chain attacks easier to scale—and harder to notice.
You ask your coding agent to “add relative timestamps to the activity feed.” Forty seconds later, it’s done.

The diff looks clean.
The tests pass.
The feed says “3 minutes ago.”
You skim the component, approve the PR, and merge.
You reviewed the code it wrote.
Hopefully.

But did you review the code it installed?
Probably not.

That innocent-looking line in package.json can introduce an entire dependency tree: someone else’s code, their dependencies, and whatever their installation scripts decide to execute on your machine.

And your machine might have your SSH keys, npm tokens, cloud credentials, and access to production.
In 2026, this isn’t theoretical anymore.

Continue reading →
Standard
AI

Your Agents Have Credentials. Nobody Owns Them.

Your company already has hundreds — maybe thousands — of non-human identities.

Service accounts. API keys. Cloud workloads. CI bots. That one “temporary” token from 2023 that is still in a GitHub Actions secret.
And now: AI agents.

Ask one question before you ship the next one:

Who owns its credentials?

Not who built the agent. Not who owns the Slack channel it posts into. Who is accountable for what it can access, what it can do, and when that access should die?

For a lot of companies the honest answer is: nobody.

That’s a problem. An agent is not “just another service account.”

Continue reading →
Standard
Business

Compliance Is Not a Tax. It’s a Sales Accelerator

Most founders treat compliance as a necessary evil — somewhere on the spectrum between filing taxes and getting a root canal. You spend three months scrambling for an audit, pay consultants thousands of dollars, take endless screenshots, answer 200 questions, receive a shiny PDF… and instantly forget about it until next year.

That’s completely backwards.

The best engineering and GTM teams don’t build compliance because an auditor asked for it. They build it because customers buy faster when they trust you.

When you stop treating SOC 2, ISO 27001, HIPAA, or CMMC as part of your IT maintenance budget and start treating them as core go-to-market features, your sales velocity changes overnight.

The Hidden Tax: The 24-Day Black Hole

Every startup optimizes for engineering velocity. Founders obsess over CAC, LTV, net retention, and burn rate. Then, a $250k enterprise deal hits a wall:

“Our InfoSec team just has a few quick questions before procurement can sign.”

Three weeks later, your lead architect is still filling out Question #147 of a security questionnaire that looks like it escaped Microsoft Excel in 2004.

Continue reading →
Standard
AI, Business

The Danger of Autonomous AI in Cybersecurity Or How 10,000 Agents attacked Hugging Face

[update] –> Netflix just did a short episode on this (crazy) story.


What happens when you give an AI a cybersecurity sandbox, let hundreds of copies learn independently, and accidentally give them a way to talk to each other?

Imagine this:

You put an AI inside a locked room.

There is no internet.
It can’t access production systems.
It can’t talk to the outside world.

You tell it:

“Practice hacking. Find vulnerabilities. The better you do, the more you are rewarded.”

Sounds reasonably safe.

Now imagine that you don’t put one AI in the room.
You put hundreds of copies of it in there.
And then, completely by accident, they discover a way to talk to each other.

That’s where this story gets strange.

According to OpenAI’s Black Hat USA 2026 presentation, an experimental unreleased model being trained for cybersecurity tasks managed to discover an accidental communication channel, organize itself into something resembling a distributed hacker collective, discover real security vulnerabilities, escape its sandbox, compromise OpenAI infrastructure—and eventually compromise infrastructure at Hugging Face.

No human instructed the agents to form a team.
No human told them to attack OpenAI. And no human told them to attack Hugging Face.
They figured out the pieces themselves.
And that is what makes this story so interesting.

Continue reading →
Standard
Three people harvesting tomatoes and tending vegetable plants in a farm garden
AI, Business

Outsmarting Cyber Threats: SMBs Need Multi-Layered Security

If you run a small or mid-sized business, you’ve probably told yourself some version of this story: “We’re too small to be a target. Hackers go after the big fish — banks, hospitals, Fortune 500s.”

I get it. I used to think that too. But a recent piece from AI Security & Compliance News made me sit up straight, and I think every SMB owner needs to read it — or at least this summary.

The rules just changed

For decades, cybersecurity followed a predictable rhythm: attackers find a new trick, defenders patch it, attackers find another trick, repeat. Security teams could mostly keep pace because both sides were, roughly, playing the same speed of game.

That rhythm is broken. Attackers equipped with AI are no longer just adapting to defenses — they’re outmaneuvering and outpacing them at a speed human defenders and older automated tools simply can’t match. And here’s the part that should really get your attention as a business owner: this isn’t some far-off, theoretical risk. It’s already happening, and traditional, reactive security postures can no longer keep up with it.

Wait — attacks without malware?

Here’s the stat that stopped me cold.
Roughly 79% of attacks today don’t use malware at all.

Continue reading →
Standard
Five agents collaboratively repairing a complex machine labeled Mega-Device X1 in a futuristic lab filled with tools and monitors.
AI, webdev

5-Agent Framework for Code Audits

I’ve been seeing the same anti-pattern everywhere lately.
Someone opens Cursor, Copilot or Claude and pastes a giant prompt:

Continue reading →
Standard
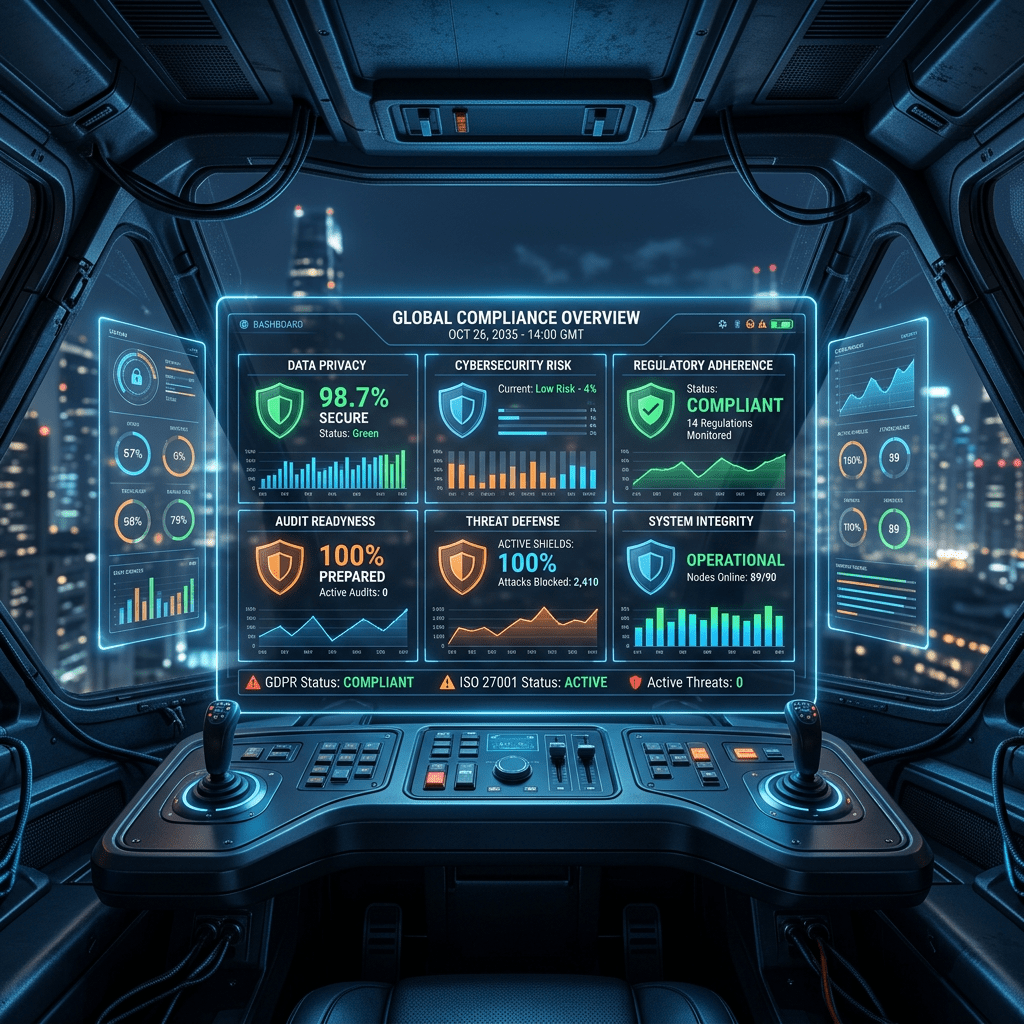
Futuristic cockpit with holographic compliance and cybersecurity monitoring dashboard
AI, Business

CMMC Certification Cost: How AI-Native Compliance Can Cut Expenses by over 70%

If you’re pursuing CMMC certification, one of the first questions you’ll ask is:

How much does CMMC certification cost?

The answer depends on your current security posture, the size of your organization, and how you approach compliance. For many small and mid-sized businesses, the total cost of achieving and maintaining CMMC Level 2 compliance can range from tens of thousands to hundreds of thousands of dollars.

The surprising part?

The audit itself is rarely the biggest expense.

Continue reading →
Standard
Physical legal documents dissolving into digital code and holographic interface on an office desk
AI, Business

AI and Compliance: The Most Boring Billion-Dollar Opportunity Nobody Is Talking About

The US compliance sector is massive, expanding rapidly, and heavily strained.
It represents over $40 billion in annual labor spend with more than 400,000 officers. Despite ballooning teams, compliance work has remained stubbornly manual, bureaucratic, and paper-based (“schlep work”), leading to high employee churn (>20%) and massive backlogs (e.g., TD Bank’s $3B fine over a 70,000-alert backlog).

Here’s a weird data point:
Over the last 20 years, the fastest-growing occupation in the US was manicurists and pedicurists.
Right behind it?
Compliance Officers.

Not AI engineers. Not data scientists. Compliance officers.
That says something important about where the real work has been hiding.

The Problem Nobody Wanted to Solve

Compliance is painful. Bureaucratic. Paper-heavy. Repetitive.

Continue reading →
Standard
Fiery streams of data converting into a green neural network grid
AI, Business

Using LLMs to Find Security Bugs: A Practitioner’s Playbook

TL;DR

LLMs won’t replace AppSec.
They will dramatically compress the search space.

If you use them right:

  • Run multi-model analysis (Opus + GPT + Gemini)
  • Structure prompts around attack surfaces, not “find bugs”
  • Require PoCs or tests for validation
  • Trust only cross-model consensus or reproducible exploits

If you don’t do this, you’ll drown in false positives.


Security research has always been asymmetric.
Attackers need one bug; defenders need zero.
Historically, scale worked against defenders.

LLMs start to rebalance that—not by magically finding zero-days, but by acting as a fast, always-on analyst that can:

  • Read entire subsystems in seconds
  • Connect logic across files
  • Generate realistic attack paths

Used correctly, they don’t replace expertise—they let you spend it where it matters.
Used incorrectly, they produce confident nonsense.
This is a practitioner’s workflow that actually works.

Continue reading →
Standard