Business

Your Insurance Carrier Is Now Your Auditor

Cyber insurance used to be a safety net. In 2026, it’s also a security exam. And the test is no longer optional.

There was a time when buying cyber insurance was simple.
Fill out a questionnaire. Pay the premium. File the PDF somewhere between your business license and that printer manual nobody has opened since 2019.

Then ransomware happened.
And insurers realized something uncomfortable: companies were buying protection against cyberattacks without necessarily doing much to prevent them. So the questions changed.

Welcome to the new underwriting reality

The 2026 underwriting bar is increasingly specific:

  • Over 90% of applications ask detailed MFA questions, including RDP, VPN, cloud, and privileged accounts. SMS-based MFA is increasingly flagged as insufficient.
  • Over 80% of carriers require EDR or MDR across all endpoints.
  • Immutable backups are becoming a hard requirement, not a nice-to-have.
  • Documented proof is replacing checkbox answers. Some renewals now involve independent audits or evidence reviews.

These figures reflect the underwriting picture in our brief; requirements vary by carrier and policy. The message, however, is clear: saying you have security is no longer enough. You need to prove it.

Continue reading →
Standard
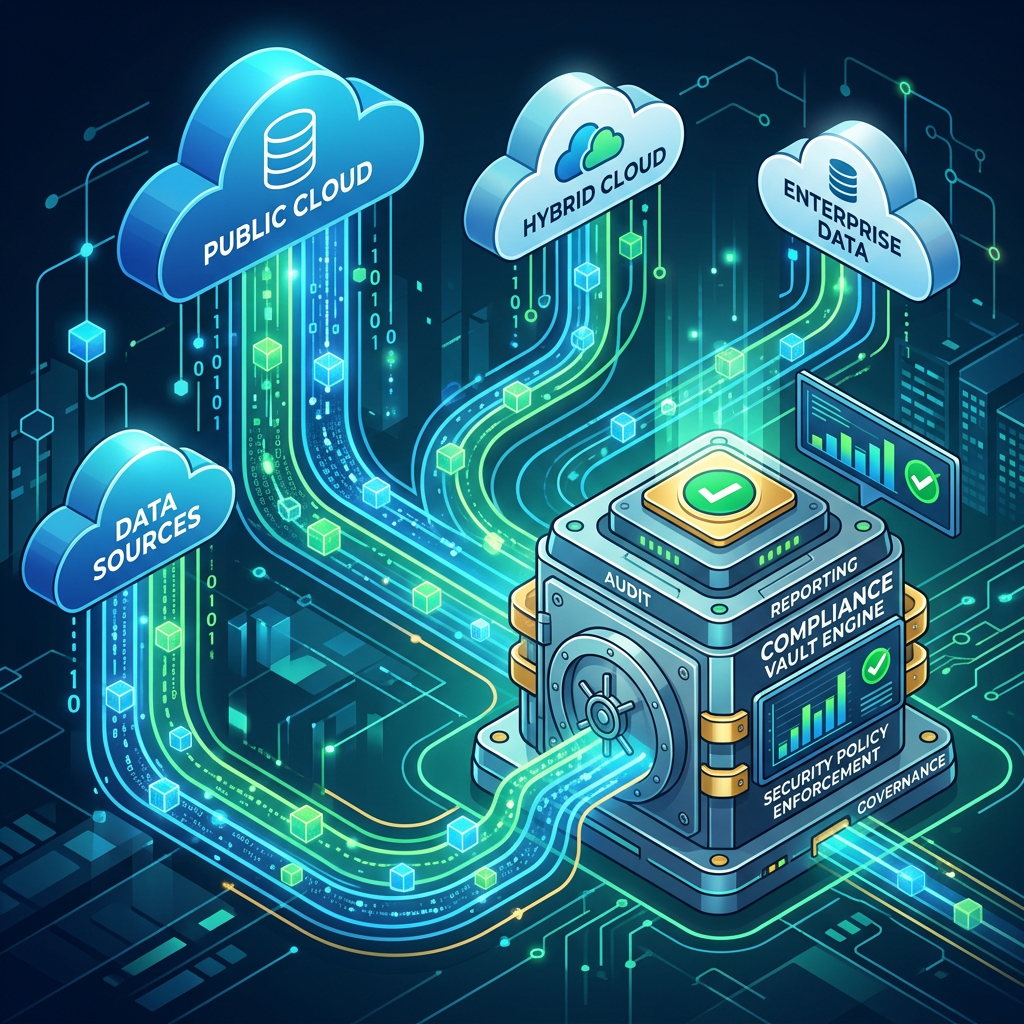
Secure data streams from public, hybrid, enterprise cloud, and data sources into a compliance vault engine
AI, Business

Automating the Audit Trail: How I Built a GitHub Screenshoter for Zero-Friction SOC 2 Compliance

It’s audit season. And if you’re a SaaS startup, you know exactly what that means.
The dreaded “Change Management” evidence request.

Some auditor sends you a list of 15 random commit SHAs from your production branch and says: “Prove to me that every single one of these was reviewed, approved, and linked to a ticket.”

Your heart sinks.

You know you’re about to spend the next four hours of your life doing the most mind-numbing task in tech: opening GitHub, finding the commit, taking a screenshot, finding the PR, taking a screenshot, finding the issue, taking a screenshot, and pasting it all into a PDF.

It’s manual. It’s painful. And it’s a complete waste of engineering time.

So, I built a tool to kill this pain once and for all: GitHub Screenshoter.

Continue reading →
Standard
AI, Business

Understanding SOC 2 Compliance: Why It’s Critical for Business

You don’t lose deals because your product is bad.
You lose them because someone in procurement asks: “Are you SOC 2 compliant?” — and you’re not.

That’s it.
Game over.

What is SOC 2?

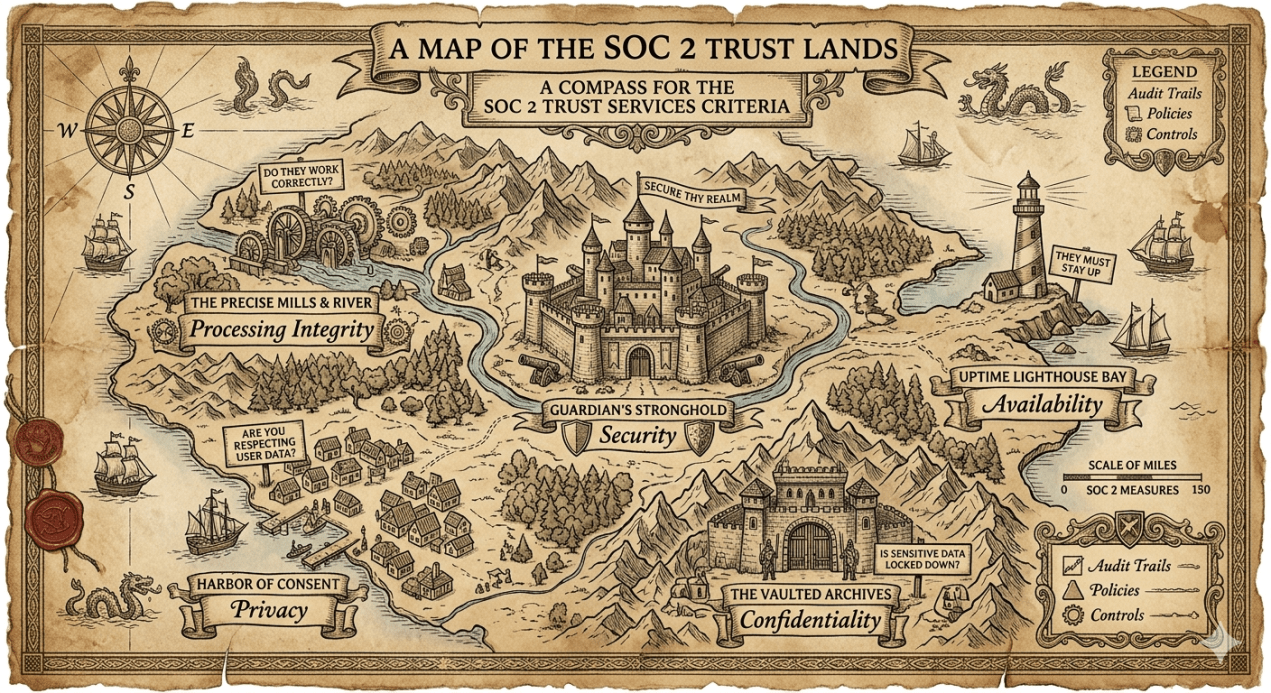
It is a security and trust standard. It proves that your company handles customer data responsibly across five areas:

  • Security – are your systems actually protected?
  • Availability – do they stay up?
  • Processing integrity – do they work correctly?
  • Confidentiality – is sensitive data locked down?
  • Privacy – are you respecting user data?

It’s not a checklist.
It’s an audit.
An external firm comes in and validates that you’re not just saying you’re secure—you actually are.

Why it matters

SOC 2 isn’t about compliance.
It’s about trust at scale.

Continue reading →
Standard